TheCyberAryan · Knowledge Base

Research, notes & field learnings.

A practical cybersecurity journal covering web application security, bug bounty methodology, offensive security tools, vulnerability research and the fundamentals behind them.

01 / RESEARCH  ·  LEARN  ·  BUILD  ·  SHARE
BY ARYAN PAREEK
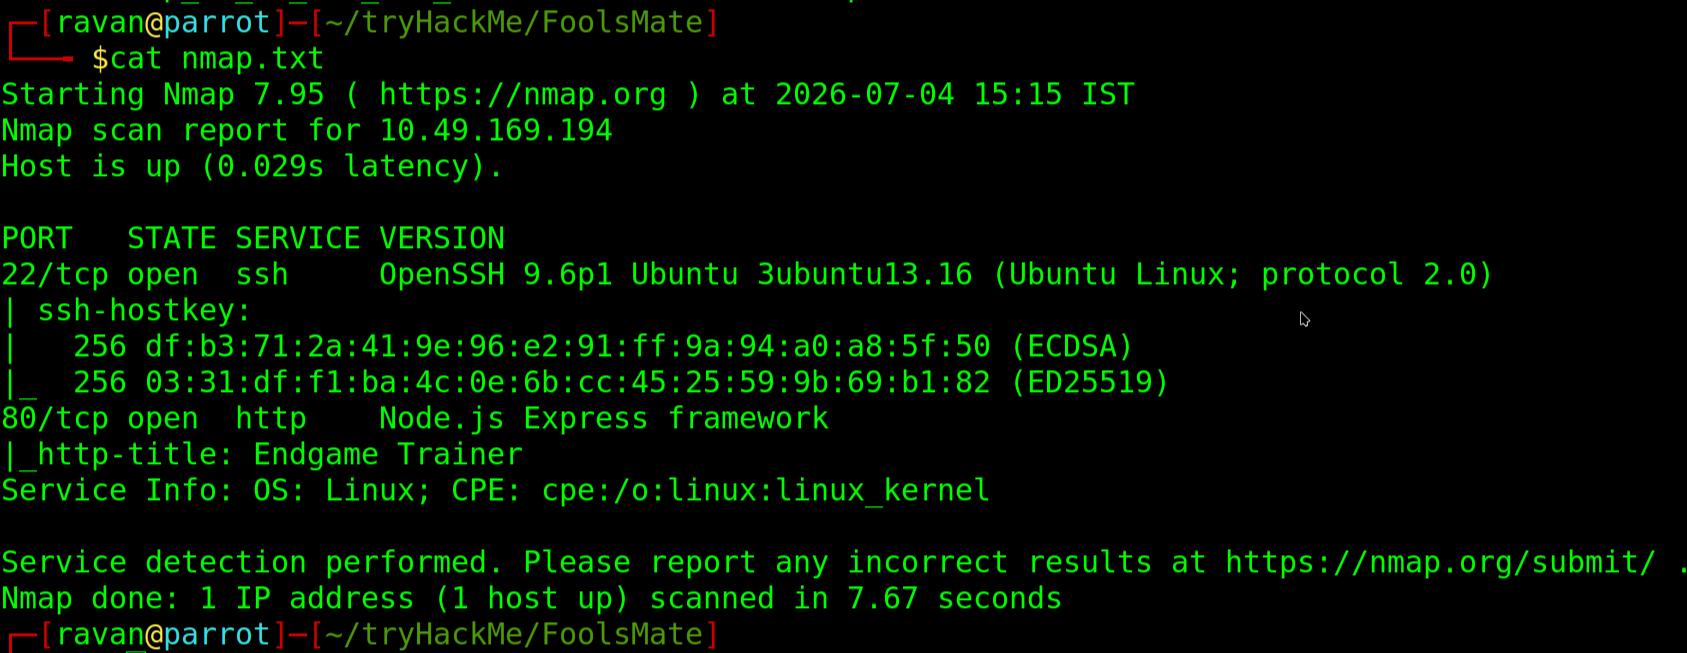
Fool's Mate TryHackMe walkthrough
Jul 4, 20268 min readTryHackMe

“I'll Shut Down Your PC If You Play That” — Fool's Mate Walkthrough

A harmless chess game threatened to shut down my PC if I made the winning move. Instead of listening, I examined the application’s backend interaction and explored an important lesson about trusting client-side controls.

Read the walkthrough ↗
Information security standards and frameworks
Jan 14, 202612 min readFrameworks

STIG, NIST and ISO

A practical introduction to three widely used approaches to security hardening, risk management and information security governance.

Read the article ↗
TheCyberAryan publication thumbnail
Nov 8, 20256 min readSQL injection

Responsible Disclosure: SQL Injection (Sanitized)

A vendor-safe case study of a discovered SQL injection in a public endpoint, with sanitized proof-of-concept notes, safe reproduction guidance and remediation using prepared statements.

Read the case study ↗
Code on a computer screen
Nov 3, 20255 min readToolkit

Starter Toolkit for Web App Pentesting

A compact introduction to tools commonly used during authorized web application assessments, including Burp Suite, Nmap, Gobuster and Nikto.

Read the toolkit ↗
Botnet illustration
Nov 20, 202512 min readThreats

What Are Botnets?

Understand how compromised devices become remotely controlled bots, how command-and-control works and why botnets are used in distributed attacks.

Read the explainer ↗
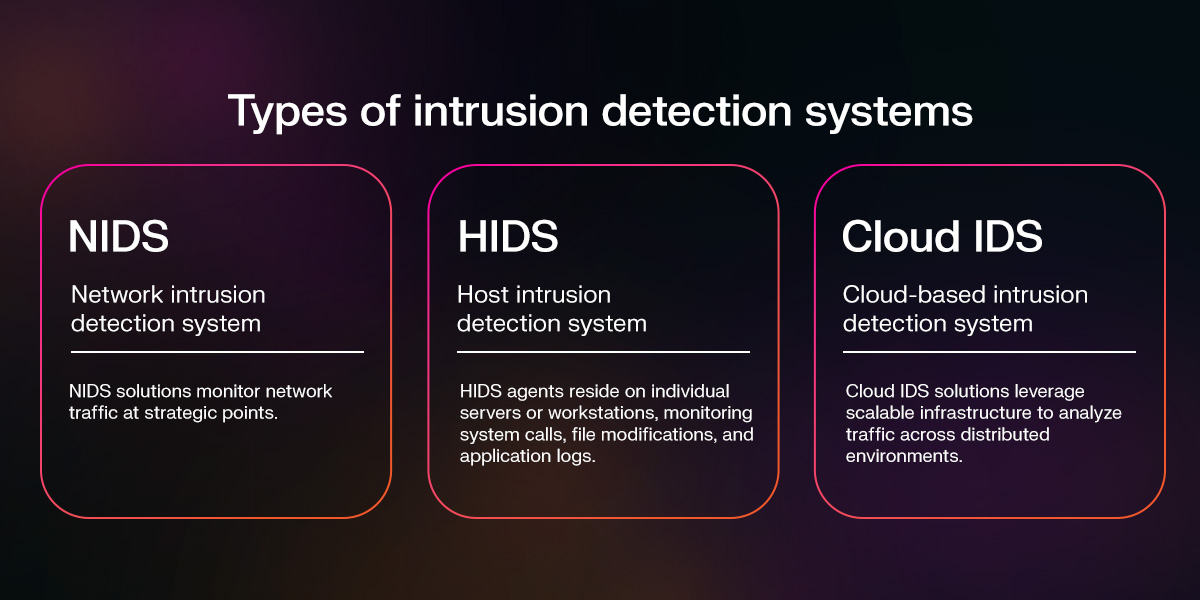
Intrusion detection systems
Dec 24, 202513 min readSecurity tools

Underrated Security Tools

A look beyond the familiar names at useful security tools that can strengthen investigation, monitoring and assessment workflows.

Read the article ↗
IDOR vulnerability concept
Nov 18, 20259 min readAccess control

What Is IDOR?

Learn how insecure direct object references and broken object-level authorization can expose resources when access checks are missing.

Read the explainer ↗
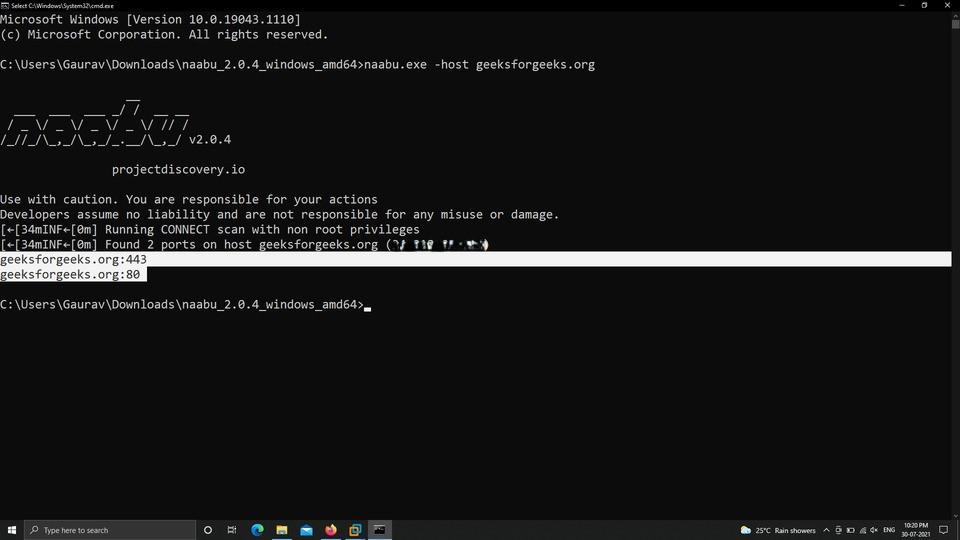
Port scanning illustration
Nov 18, 20259 min readNaabu

Naabu: Complete Usage Guide

A beginner-friendly introduction to fast port discovery with Naabu and its role in an authorized reconnaissance workflow.

Read the guide ↗
ProjectDiscovery reconnaissance tool thumbnail
Nov 20, 202511 min readNuclei

Nuclei: Full Usage Guide

Explore Nuclei templates, commonly used options and ways to integrate template-based checks into authorized security testing.

Read the guide ↗
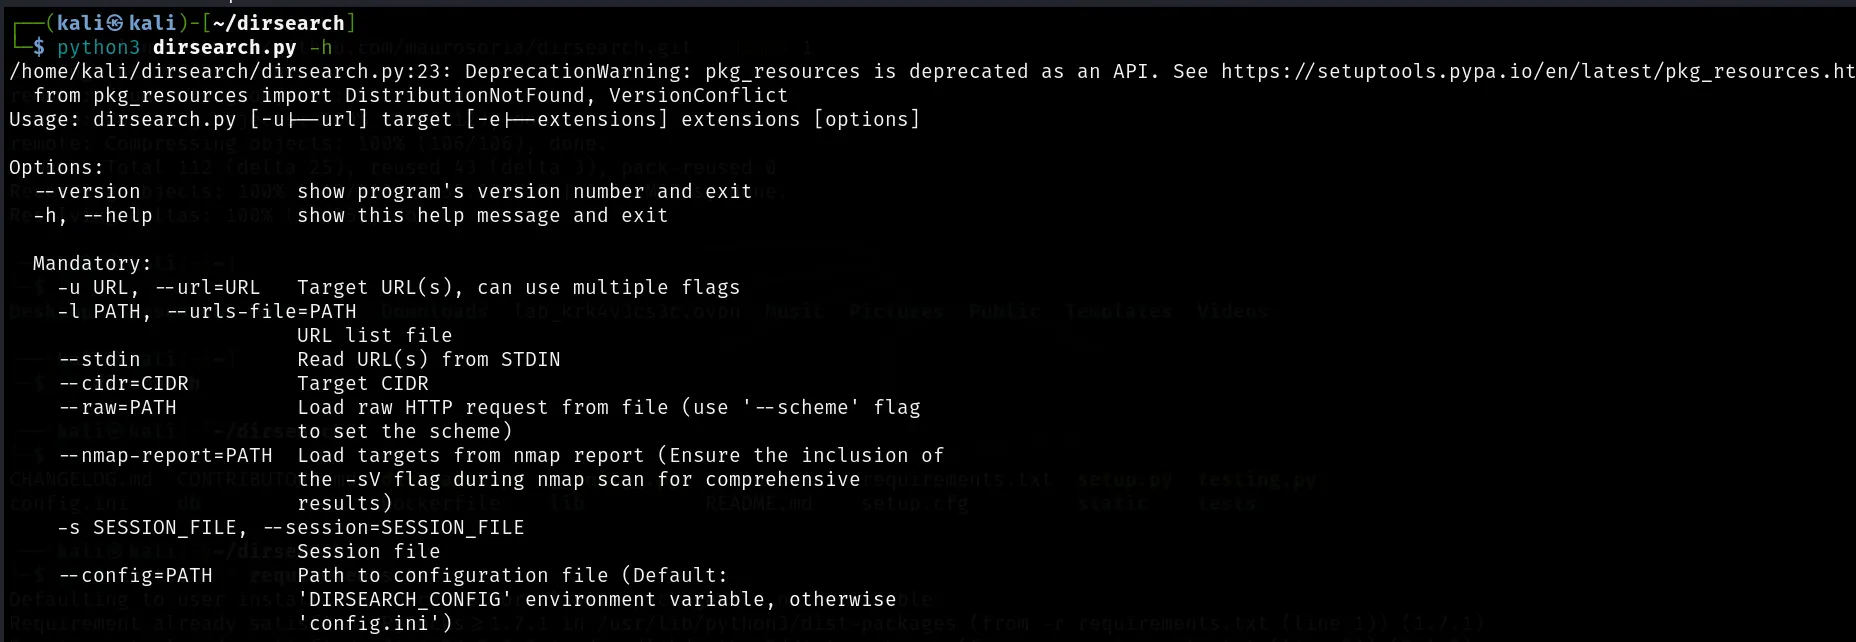
Directory discovery concept
Nov 17, 20258 min readDirsearch

Dirsearch — Zero to Hero

Understand directory and file discovery, useful options and how to interpret results responsibly.

Read the guide ↗
Nmap network scanning
Nov 18, 20257 min readNmap

Nmap Essentials

A practical introduction to common Nmap options, service discovery and network scanning fundamentals.

Read the guide ↗
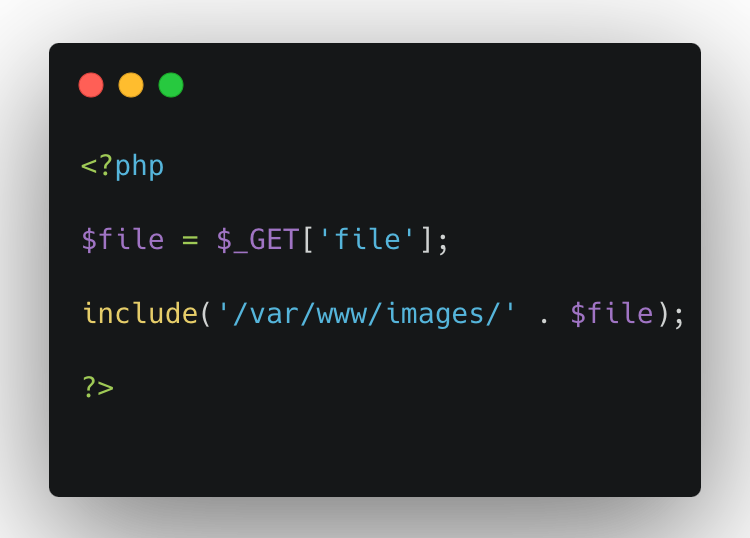
Path traversal concept
Nov 20, 20258 min readWeb security

What Is Path Traversal?

A clear explanation of directory traversal, why unsafe file path handling matters and how developers can prevent unintended file access.

Read the explainer ↗
HTTP probing tool
Nov 20, 20257 min readhttpx

httpx Essentials

Learn how HTTP probing helps identify responsive web services and enrich asset discovery during authorized reconnaissance.

Read the guide ↗
Subdomain discovery
Nov 19, 20257 min readSubfinder

Subfinder: Zero to Hero

An introduction to passive subdomain enumeration, data sources and how discovered assets fit into a broader recon process.

Read the guide ↗
Cross-site scripting illustration
Nov 9, 20255 min readXSS

Reflected XSS — Responsible Disclosure

A safe, redacted explanation of a reflected cross-site scripting discovery, its impact and responsible reporting considerations.

Read the case study ↗
SQL injection concept
Nov 7, 20256 min readSQL injection

How I Found a (Sanitized) SQLi in a Search API

A sanitized SQL injection discovery walkthrough, focusing on safe validation, clear evidence and practical remediation.

Read the case study ↗
No articles match your search. Try another keyword or select “All”.